Modern API Security: Human Knowledge and Agent Skills
Building APIs is easier than ever, thanks to AI-based software development. But how certain are you that the API you have just created is secure? Did your coding agent follow the latest security best practices? Are you sure that your authorization logic is secure and easy-to-audit? Does your test suite accurately test for potential security issues? Does the API have a solid CORS policy applied, or is it wide open to abuse?
In this workshop, you will gain the necessary knowledge and insights to stay on top of security in your APIs. We dive into API security from a Human-first perspective, helping you understand how security vulnerabilities affect APIs and how you can design and build your APIs to withstand such attacks. We complement this knowledge-based angle with practical guidance on how to ensure your AI agents follow these security best practices. We also focus on setting up accurate and relevant test suites, to make sure your API is secure, now and in the future.
The workshop consists of in-depth lectures, complemented with real-world demos, fun quizzes, and hands-on attacker & defender labs. During this hands-on training, we'll explore:
- The security model of API-based web applications
- Recognizing and addressing authorization failures
- Fixing Broken Object Level Authorization (BOLA)
- Understanding Broken Object Property Level Authorization (BOPLA)
- Agent guidelines for implementing secure and understandable authorization
- Testing the security of APIs that use JWTs
- Best practices for making JWTs secure in modern APIs
- Testing guidelines to uncover JWT pitfalls
- Understanding Cross-Origin Resource Sharing (CORS)
- Configuring secure CORS policies for various use cases
- Agent guidelines to protect your API against unauthorized cross-origin access
- Tracking user authentication securely with sessions or tokens
- Relying on OAuth 2.0/2.1 for securing APIs
- Advanced OAuth 2.x scenarios
- Quizzes and labs to make learning stick
- Q & A throughout the workshop to clear up any doubts
This workshop is about more than theory. We're all about giving you practical security tips you can use right away as an API developer. We dig into the root causes of API threats and how to handle them. We don't just skim the surface of problems and solutions - we get into the why's and how's, looking at common fixes, why some fall short, and which ones are currently the best way to go. Of course, we complement these insights with practical guidance and sample skills/repository guidelines you can use to get your AI agents on the same page.
By the end of this workshop, you'll be up-to-speed on the best practices for API security. You'll also leave with a handy list of steps to check and boost the security of your applications, along with the capability of making your AI agents consistently apply these best practices.
Who should attend?
This training is perfect for developers and architects who work a lot with APIs. If your role involves building, testing, or designing modern apps, this workshop will give you a thorough, up-to-date understanding of the best ways to keep things secure. We'll often use NodeJS, Flask, and Spring Boot in our code examples and demos, but you'll easily be able to apply what you learn to other languages and frameworks.
Testimonials
These testimonials from previous workshops give you a good idea of what to expect:
Trainer is great and an expert in the domain. All of the topics are very relevant. Practical examples for most of the topics. Excellent communication and addressing of questions.
Even though the topic is broad, there was no single moment where my focus went astray. Philippe talks in a way to keep you interested to listen to him.
I liked the pleasant and relaxed way of speaking and the fresh style of presentation of this kind of dry stuff :)
Philippe is a friendly and knowledgeable trainer and delivered an interesting course that was well presented. Questions were answered promptly and in a detailed way.
Prerequisites
To participate in this training, you should have some experience with building API-based applications. Knowledge of application security can be helpful, but is not required.
Computer setup
To participate in the lab sessions, participants need a computer with a full-featured modern browser installed (preferably Chrome).
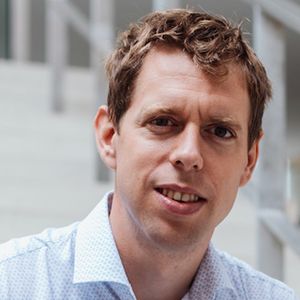
Philippe De Ryck specializes in making web security accessible to developers and architects, leveraging his Ph.D. from KU Leuven to inform his comprehensive understanding of security challenges. As the founder of Pragmatic Web Security, he provides practical security training and consulting services to organizations worldwide.
His online course platform offers a self-paced approach to learning about security. Philippe also actively helps shape OAuth 2.0 best practices as the co-author of the best practices for browser-based apps specification.
Philippe is recognized as a Google Developer Expert, acknowledging his contributions to web application and API security. He also organizes SecAppDev, an annual week-long application security course in Belgium.